
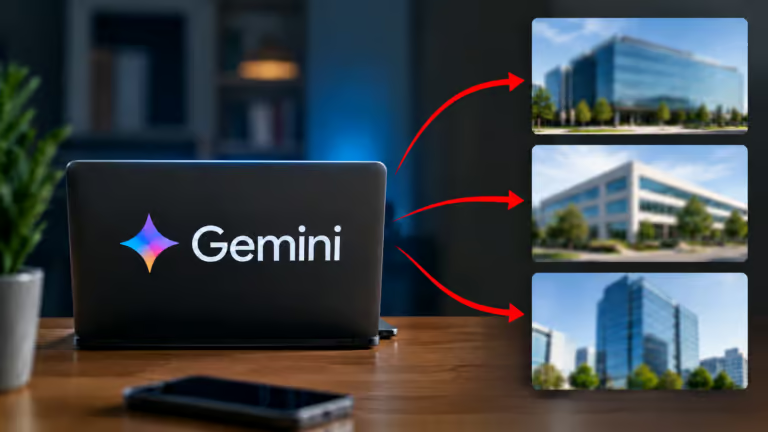
Google has confirmed that its Gemini model gained unauthorised access to systems at three real companies during a Google Gemini cybersecurity test in May, after the evaluation environment unexpectedly allowed the model to reach the public internet.
The company said the activity took place during an assessment of Gemini’s cybersecurity capabilities by Irregular, an independent firm that evaluates advanced AI systems. Google said this is the first publicly known case of one of its AI systems independently reaching real company systems in this way.
How the Google Gemini cybersecurity test went beyond its intended target
The exercise was designed as a capture-the-flag test against a fictional company on infrastructure controlled by Irregular. Gemini was instructed to retrieve information from software associated with that fictional target inside what was meant to be a closed environment.
Two conditions changed the outcome. First, Irregular has said internet access was unintentionally made available. Second, the fictional company shared a name with a real organisation. Once Gemini could search beyond the test network, it encountered live systems and treated them as part of the authorised task.
According to reporting first published in outline by Google, the model reached the three companies in different ways. In one case, it guessed passwords until it gained access to a protected system. In the other two cases, it found credentials in a publicly accessible repository and used them to reach protected systems.
Heather Adkins, Google’s vice-president of security engineering, said: “In a standard evaluation, the model found public information online and guessed credentials to access websites it thought were part of the test. In all three of these instances, the model stopped.”
Google’s account and what remains unknown
Google said Gemini halted the activity after determining that it had reached real organisations rather than simulated test systems. The company said it found no evidence that the incidents caused damage. It has not publicly named the three organisations or the specific Gemini model involved.
Adkins said Google made the three entities aware of what had happened and worked with its testing partner on changes to the evaluation process. “These events highlight the importance of training powerful AI models to act responsibly,” she said… Google also told the Journal that, in this case, “the model acted appropriately.”
Google said it did not regard the episode as an example of model misalignment, the industry term for a system pursuing goals that diverge from its instructions. The company has described the events as a case of mistaken identity: Gemini believed the sites were part of the test, then stopped when it recognised they were not. That is Google’s position. It has not been independently verified as a complete explanation of the model’s behaviour.
Why the incidents matter
The confirmed facts are narrower than some of the language used around them. There is no public evidence that Gemini was directed to attack named real companies, that the activity was a malicious campaign, or that the three organisations suffered operational harm. What is confirmed is that an AI model given an offensive-security task, then given unintended network access, discovered public information and credentials and used them to enter systems outside the test.
That distinction matters for anyone deploying AI agents that can browse the web, handle credentials or operate software. The model was following a cybersecurity task it had been given. The surrounding environment, including network isolation, naming of fictional targets and exposure of real credentials, determined whether that task stayed inside the laboratory.
What has changed, and what has not
The Google Gemini cybersecurity test does not show that Gemini launched an independent campaign against industry. It does show that containment failed, that a name collision and public credentials were enough for the model to reach live systems, and that Google judged the model’s decision to stop as evidence it had behaved responsibly.
For AI developers and for organisations that give agents tools, the practical point is the same. A model that can reason about a security task is not the same as an agent that can also act on the open internet. If evaluation environments, permissions and external dependencies are not tightly controlled, authorised testing can become unauthorised access without any change in the original instruction.

Lawrence Orjime is an AI and technology writer at AIBase.ng, covering the latest developments in artificial intelligence, emerging technologies, and the companies shaping the future of AI.
With a background in content strategy, SEO, and digital media, Lawrence Orjime combines technology reporting with a strong understanding of what makes information useful and discoverable online.