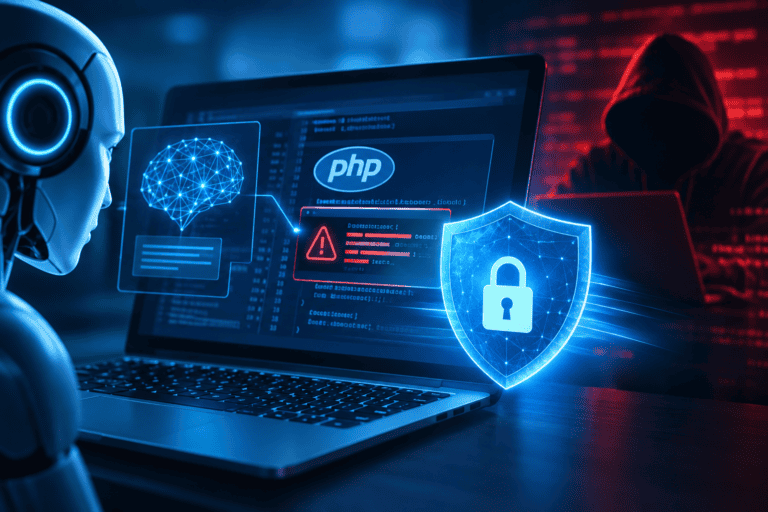
Artificial intelligence is playing an increasingly important role in cybersecurity after researchers, supported by advanced AI tools, helped uncover critical security vulnerabilities in PHP, a programming language widely used to power websites and web applications.
OpenAI announced on 21 October that its Patch the Planet initiative had helped coordinate a response involving software maintainers, security researchers and technology companies. The effort enabled teams to prepare fixes and protective measures before the vulnerabilities were publicly disclosed.
The discovery highlights how AI can help security experts identify weaknesses in widely used software. However, it also raises concerns that similar capabilities could help cybercriminals develop attacks more quickly.
Critical PHP vulnerabilities trigger urgent action
PHP is a widely used, open-source programming language that runs on web servers and supports many websites and online services.
According to cybersecurity researchers at Wiz, two critical PHP vulnerabilities could let attackers execute malicious code remotely on affected servers without first authenticating. Depending on the system and its configuration, successful exploitation could put sensitive data and website operations at risk.
PHP maintainers publicly disclosed the vulnerabilities on 21 October, when they released security updates to address the issues. The flaws are tracked as CVE-2026-109618 and CVE-2026-109619.
The severity of the findings prompted security organisations to urge affected operators to act quickly. Leaving vulnerable systems unpatched could expose them to attacks as technical details become more widely available.
How AI helped uncover the weaknesses
OpenAI said a researcher at Calif identified a critical flaw using GPT-5.6 Sol as part of the Patch the Planet initiative. OpenAI’s announcement said Wiz independently discovered and reported both vulnerabilities.
PHP maintainers, security researchers, and companies including OpenAI, Wiz, and Cloudflare addressed the findings through cooperation.
Rather than immediately publishing technical details, the participants coordinated their work to allow time to investigate the vulnerabilities, test fixes, and prepare protective measures.
Cloudflare said it deployed web application firewall protections before public disclosure, helping protect affected systems while operators worked to update their software.
The coordinated approach demonstrates why responsible vulnerability disclosure matters: identifying a security flaw is only the first step. Developers and service providers also need time to develop, distribute, and apply effective fixes.
Why the discovery matters
The incident illustrates the potential scale of AI-assisted cybersecurity research.
AI tools can help researchers analyse complex code, identify suspicious patterns and investigate vulnerabilities that might otherwise require substantial time and specialist expertise to uncover.
But the same capabilities can create risks. Once vulnerabilities are understood, malicious actors may attempt to develop tools that exploit unpatched systems.
OpenAI said it believed it identified the vulnerabilities before attackers did, giving defenders time to prepare protections in advance. This is the company’s assessment; it does not prove that no attacker knew about the flaws beforehand.
The case also underlines the importance of supporting open-source software maintainers, many of whom must manage security reports and updates with limited resources.
Read: Anthropic Unveils Mythos AI Model in New Cybersecurity Push
What website owners should do?
PHP maintainers have released updates addressing the vulnerabilities. Organisations that operate PHP-based websites should identify the versions they use and follow the official security guidance to determine which updates apply.
Recommended actions include:
- Update promptly: Install the appropriate security release for the PHP version in use.
- Check hosting arrangements: Contact hosting providers or technical teams if responsibility for updates is unclear.
- Review additional protections: Apply relevant security guidance from trusted providers while updates are being deployed.
- Assess potential exposure: Organisations with internet-facing systems should prioritise remediation and consider whether further investigation is necessary.
Temporary protections can reduce risk, but they should not automatically replace installing the appropriate security updates.
OpenAI proposes a broader approach to AI-driven security
Beyond the PHP incident, OpenAI is proposing a coordinated framework for handling serious vulnerabilities as AI tools become more capable.
The proposed approach includes validating reported flaws, working with software maintainers to develop and test fixes, notifying relevant organisations in stages, preparing protective measures and publishing guidance once updates are ready.
OpenAI also announced a $1 billion commitment to subsidised access through its Daybreak initiative for frontline defenders, aimed at helping organisations with limited security resources.
The company is inviting feedback from researchers, software maintainers and other security professionals to improve its proposed framework.
Read also: Researchers Expose Gaps in ChatGPT’s Image Safety Controls
The future of AI and cybersecurity
The PHP vulnerabilities offer a clear example of AI’s dual role in cybersecurity: the technology can strengthen defences, but it can also increase the capabilities available to attackers.
The outcome will depend not only on how effectively AI identifies weaknesses, but also on how responsibly those findings are handled and how quickly affected organisations apply fixes.
For now, the priority is straightforward: website operators should follow official guidance, install the appropriate security updates and verify that their systems are protected.
The broader lesson is that AI can help find hidden security weaknesses, but collaboration, responsible disclosure and timely patching remain essential to keeping the internet secure.
AI Writer
Bio: Joseph Michael is an MBA graduate in Marketing from Ladoke Akintola University of Technology and a passionate tech enthusiast. As a professional writer and author at AIbase.ng, he simplifies complex AI concepts, explores digital innovation, and creates practical guides for Nigerian learners and businesses. With a background in marketing and brand communication, Joseph brings clarity, insight, and real-world relevance to every article he writes.